Gnosis Safe Incident Exposes DeFi’s Weakest Layer
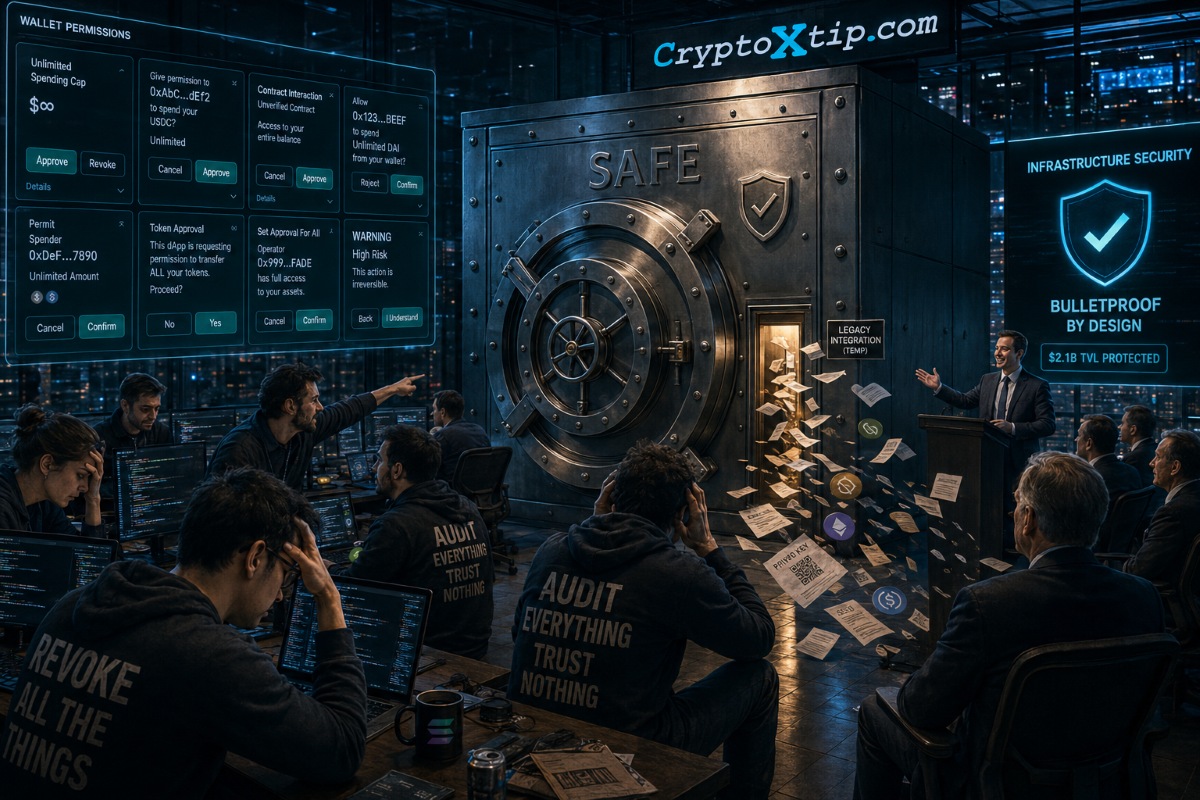
A recent exploit involving a Gnosis Safe module and roughly $3 million in losses is reminding crypto users that trusted infrastructure can still become a critical vulnerability.
Decentralized finance has spent years trying to solve the problem of trust.
Ironically, some of its biggest failures continue happening precisely where users feel safest.
A recent security incident involving a Gnosis Safe-related module and estimated losses approaching $3 million has once again exposed one of DeFi’s most uncomfortable realities: even widely respected infrastructure can become a major attack surface.
The exploit reportedly targeted an external module integrated with Safe smart wallet infrastructure rather than the core Safe contracts themselves. Early security analysis from blockchain investigators and DeFi security researchers suggested the incident involved compromised permissions tied to modular wallet functionality, allowing attackers to drain funds from affected wallets.
While the technical details continue evolving through post-incident analysis, the broader industry reaction has already become familiar. Developers issue emergency warnings. Security researchers publish transaction breakdowns. Users revoke permissions in panic. Crypto Twitter briefly transforms into a crowdsourced digital crime scene investigation unit operating almost entirely on caffeine and suspicion.
Then the deeper realization arrives: trusted infrastructure may be decentralized, audited, battle-tested, and still dangerously vulnerable through surrounding integrations.
The Problem Was Not Necessarily Safe Itself
One important distinction emerged quickly after the incident.
The exploit does not appear to have compromised the core architecture of Safe itself, formerly known as Gnosis Safe, which remains one of the most widely used multisignature wallet infrastructures in crypto. Safe products are heavily integrated across DAOs, treasury systems, institutional custody frameworks, and DeFi protocols.
Instead, the weakness reportedly involved a third-party module connected to Safe’s flexible permission system.
That difference matters technically, but for users experiencing drained wallets, the nuance can feel emotionally irrelevant.
Modern DeFi increasingly relies on modular infrastructure. Wallets connect to plugins, modules, bridges, automation layers, governance systems, account abstraction tools, staking integrations, and transaction relays. Each additional feature improves usability or functionality. Each additional connection also expands the potential attack surface.
This is one of the defining tensions inside decentralized finance.
Crypto users want systems that are secure, decentralized, programmable, fast, composable, user-friendly, capital-efficient, and fully interoperable across dozens of chains simultaneously. Unfortunately, software engineering still insists on involving trade-offs.
The more complex DeFi infrastructure becomes, the more difficult it becomes to fully model every possible interaction between interconnected systems.
Security researchers have warned about this problem for years. In many cases, the highest risk no longer comes from core protocol contracts themselves, but from integrations, permission structures, governance mechanisms, and peripheral tooling surrounding otherwise secure infrastructure.
DeFi’s “Trust Layer” Is Growing Larger
The incident also highlights how much hidden trust already exists inside supposedly trust-minimized systems.
Safe has become deeply embedded across the crypto ecosystem because institutions, DAOs, and advanced users trust its architecture. That trust is not irrational. The platform has built a strong reputation over years of production-level usage and extensive auditing.
But trust in crypto rarely exists in isolation anymore.
Users trust wallet infrastructure. They trust modules connected to wallets. They trust transaction simulators, front-end interfaces, governance tooling, and smart contract permissions they often barely understand.
At some point, many DeFi users stop independently verifying systems and instead rely on ecosystem reputation.
That behavior is entirely human. It is also where systemic vulnerabilities often emerge.
Traditional finance operates similarly. Most people do not inspect bank software architecture before using online banking apps. Trust eventually becomes abstracted into brand credibility and institutional reputation.
Crypto promised a more transparent alternative, yet much of the ecosystem increasingly functions through layered assumptions users cannot realistically audit themselves.
The difference is that traditional banking failures usually involve customer support phone numbers and legal recourse. DeFi failures often involve Telegram alerts and irreversible transactions disappearing into newly created wallets faster than anyone can type “funds are safu.”
Why Modules and Permissions Matter
Safe’s modular structure exists for legitimate reasons.
Large crypto organizations frequently require flexible treasury management systems capable of handling automated payments, multisignature approvals, role delegation, transaction scheduling, and cross-chain operations. Modules allow developers to extend wallet functionality far beyond simple storage.
That flexibility helped transform Safe into critical infrastructure across decentralized finance.
Yet modularity also creates additional complexity around permissions management.
In blockchain systems, permissions effectively determine who or what can move assets under specific conditions. A compromised module with elevated permissions can become extraordinarily dangerous because users may unknowingly authorize broad operational access during setup processes.
Security experts repeatedly emphasize that smart contract exploits increasingly target human assumptions rather than purely cryptographic weaknesses.
Attackers understand that users often approve permissions without fully reviewing contract logic, especially when interacting with familiar infrastructure brands.
The result is an ecosystem where operational convenience sometimes quietly outpaces security awareness.
This trend has accelerated as account abstraction, smart wallets, and programmable wallet infrastructure become more advanced. Crypto onboarding improves when wallets behave more like modern applications rather than raw cryptographic tools.
But every abstraction layer introduces additional complexity requiring security oversight.
The industry wants Web3 products that feel seamless enough for mainstream adoption while retaining self-custody principles. Achieving both simultaneously remains remarkably difficult.
The DeFi Security Problem Is Evolving
Crypto security discussions historically focused heavily on smart contract audits.
Audits remain important, but the industry increasingly understands that audits alone do not eliminate systemic risk.
Many recent exploits across DeFi involved issues tied to governance manipulation, bridge infrastructure, oracle dependencies, front-end compromises, social engineering, or permission abuse rather than simple coding mistakes.
The attack surface has expanded alongside ecosystem sophistication.
DeFi protocols now resemble interconnected financial operating systems rather than isolated applications. Liquidity flows across multiple chains, wallets interact with dozens of protocols simultaneously, and automation tools execute complex transaction logic continuously.
Under those conditions, even highly respected infrastructure can become vulnerable through secondary integrations.
The Safe-related incident therefore represents something larger than a single exploit. It reflects a structural challenge facing the entire DeFi sector as it matures.
Protocols increasingly compete on features, interoperability, and user experience. Security complexity grows alongside that competition.
Meanwhile, attackers continue operating with extraordinary financial incentives.
Blockchain security firms estimate that billions of dollars have been lost across exploits, phishing attacks, bridge compromises, and smart contract vulnerabilities over recent years. Every successful attack teaches future attackers where ecosystems remain operationally fragile.
And unlike traditional cybercrime, crypto exploits settle instantly into globally transferable assets.
That tends to attract motivated participants.
Users Are Becoming More Security Conscious
One potentially positive development is that crypto users are gradually becoming more sophisticated about operational security.
Wallet permission revocation tools, transaction simulation platforms, multisig treasury practices, hardware wallet adoption, and formal security reviews are increasingly common among serious DeFi participants.
Institutional players entering crypto have also pushed infrastructure providers toward stronger operational standards, insurance frameworks, and risk management processes.
Still, retail users often remain vulnerable to interface complexity and permission confusion.
Most users cannot realistically analyze smart contract architecture before interacting with applications. They rely on ecosystem reputation, social consensus, and perceived legitimacy.
The next major challenge for DeFi may not simply involve scaling infrastructure, but scaling trust and security understanding at the same pace as usability improvements. As noted recently in additional ecosystem coverage at Article Partners
That challenge becomes harder as crypto applications increasingly resemble mainstream fintech experiences while still carrying fundamentally irreversible settlement mechanics underneath.
What This Means
The recent Safe-related security incident is another reminder that DeFi’s greatest vulnerabilities often emerge not from obvious scams, but from trusted infrastructure operating inside increasingly complex ecosystems.
Even audited and widely respected systems can become vulnerable through connected modules, integrations, and permission structures that expand operational risk beyond the core protocol itself.
For users, the lesson is uncomfortable but important.
Security in decentralized finance no longer depends solely on choosing reputable platforms. It increasingly depends on understanding how multiple layers of infrastructure interact — and where hidden permissions may exist inside those relationships.
For the broader industry, the incident reinforces a larger reality.
Crypto has become remarkably effective at building open financial systems. Building systems that remain both open and safely manageable at scale is proving significantly harder.
DeFi still offers extraordinary innovation potential. But every new layer of convenience, interoperability, and automation also creates new places where trust quietly accumulates.
And in crypto, concentrated trust has a habit of eventually becoming someone else’s attack vector.
Related Articles
More stories you may want to explore.


Sponsored Placements